Your auditor asks for 12 months of access logs. Export them in 30 seconds. They verify the chain themselves.
SHA-256 hash chaining, immutable WORM storage, EU data residency, open-source verifier. 8 compliance frameworks included: DORA, GDPR, NIS2, the EU AI Act, ISO 27001.
Built for engineering and compliance teams who need evidence an external auditor will actually accept, not logs only the people who wrote them can read.
import { AuditRails } from '@auditrails/node';

const audit = new AuditRails({ apiKey: 'at_live_...' });

await audit.log({
  action: 'user.login',
  actor_id: 'usr_123',
  resource: 'session',
  metadata: { ip: '192.168.1.1' }
});{
"status": "ok",
"log_id": "01HXYZ...",
"chain_seq": 42,
"hash": "a3f2b8c1..."
}Open source verification: every export's hash chain re-verifies locally with auditrails/verifier (Go, MIT), without depending on us.
How it works
Install the SDK, log events, export verifiable evidence.
Install the SDK
Add our SDK to your project with a single package install. Available for Node.js, Python, Go, and PHP.
Send audit events
Call one function to log any action. We handle enrichment, hash chaining, and immutable storage automatically.
Pass your audit
Use the compliance dashboard to search logs, verify chain integrity, and export reports for your auditors.
Tamper-evident by design
Every log is cryptographically chained. Try tampering with one, watch the cascade.
Cryptographic hash chain
Every log links to the previous one via SHA-256. Tampering with one record breaks the chain.
user.created
role.assigned
data.exported
user.deleted
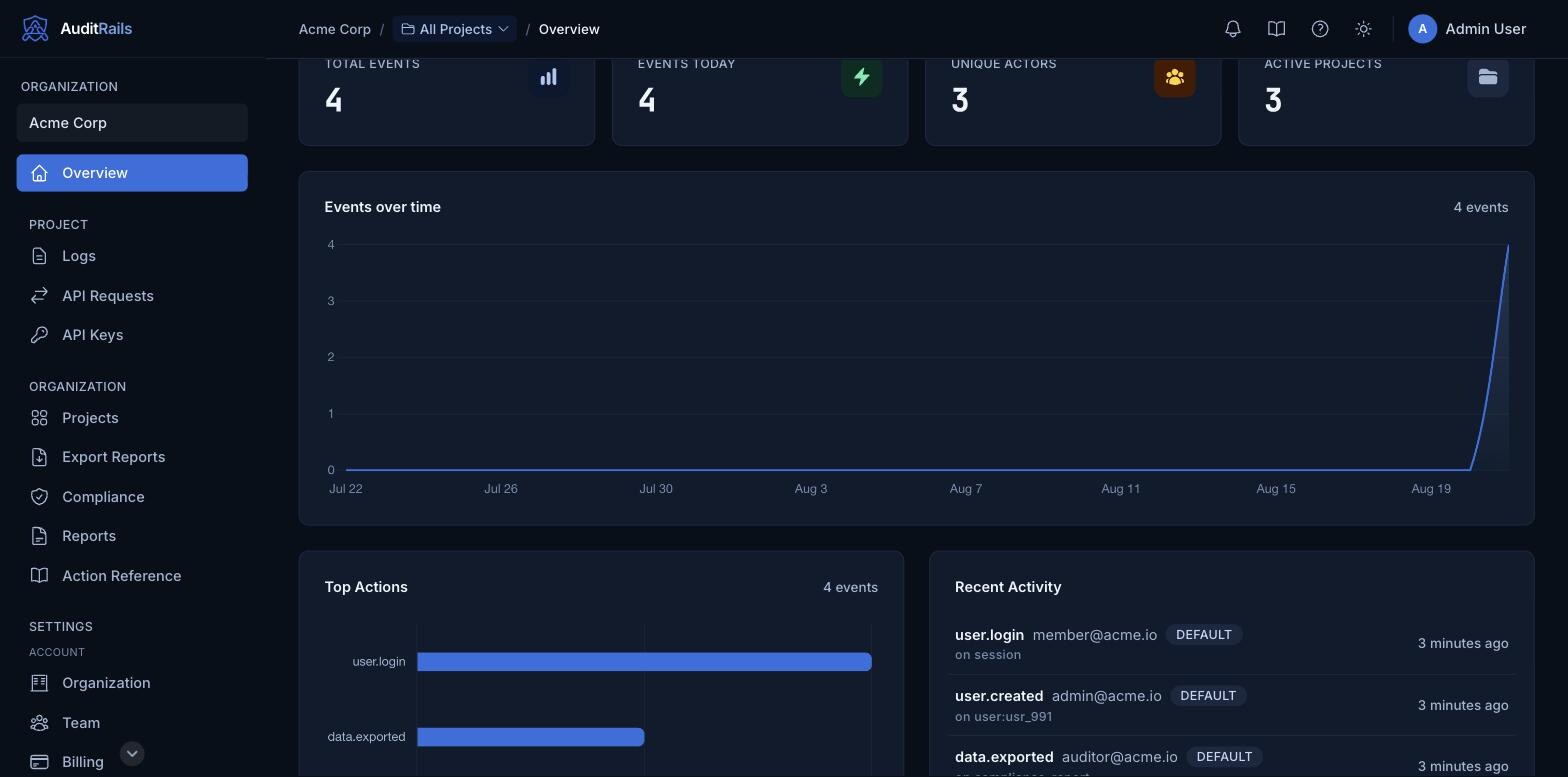
See it all in your dashboard
Every event, chain-verified in real time. Search, export, and prove compliance without leaving the tab.
Six primitives. No vague promises.
SHA-256 hash chaining. S3 Object Lock WORM storage. ClickHouse-backed search in milliseconds. Hard tenant isolation. A compliance dashboard your auditor can use directly. 4 native SDKs.
Hash Chaining
Every log entry is cryptographically chained using SHA-256. Tampering with any record breaks the chain and is instantly detectable.
WORM Storage
Logs are written to immutable, write-once-read-many storage with object lock. Once written, they cannot be modified or deleted.
Real-time Search
Search and filter millions of audit events in milliseconds. Full-text search across actions, actors, resources, and metadata.
Multi-tenancy
Built-in tenant isolation at every layer. Every API key maps to a tenant. Data is never co-mingled between organizations.
Compliance Dashboard
Real-time visibility into your audit trail. Chain verification, export for auditors, and role-based access controls built in.
4 SDKs
Node.js, Python, Go and PHP install straight from npm, PyPI, the Go proxy and Packagist. Drop in 5 lines of code and start logging in minutes.
Where the data is
The first question an Italian DPO asks, so the answer is here rather than at the bottom of a legal page.
Region and providers
Durable audit-log storage is in AWS eu-central-1 (Frankfurt, Germany), an explicit EU-first choice on every plan. The application and database layer runs on self-hosted infrastructure at Hetzner, also EU-based. From AWS we use S3 and SQS only.
Immutability and retention
S3 Object Lock in Compliance mode, not Governance: no one, including our administrators and AWS' own root account, can shorten a retention lock or delete a log before it expires. The default window is seven years.
Encryption
The durable copy in S3 is encrypted at rest with AWS KMS (SSE-KMS), and every connection between services uses TLS.
Backups
Nightly PostgreSQL and Cassandra backups to a separate, dedicated storage location. Restores are tested, not just scripted: the last drill, on August 25, 2026, restored both databases and confirmed an exact row-count match.
Start your log today
30 days free, no credit card. The first event in production takes an afternoon to write.
No credit card required. Cancel any time.